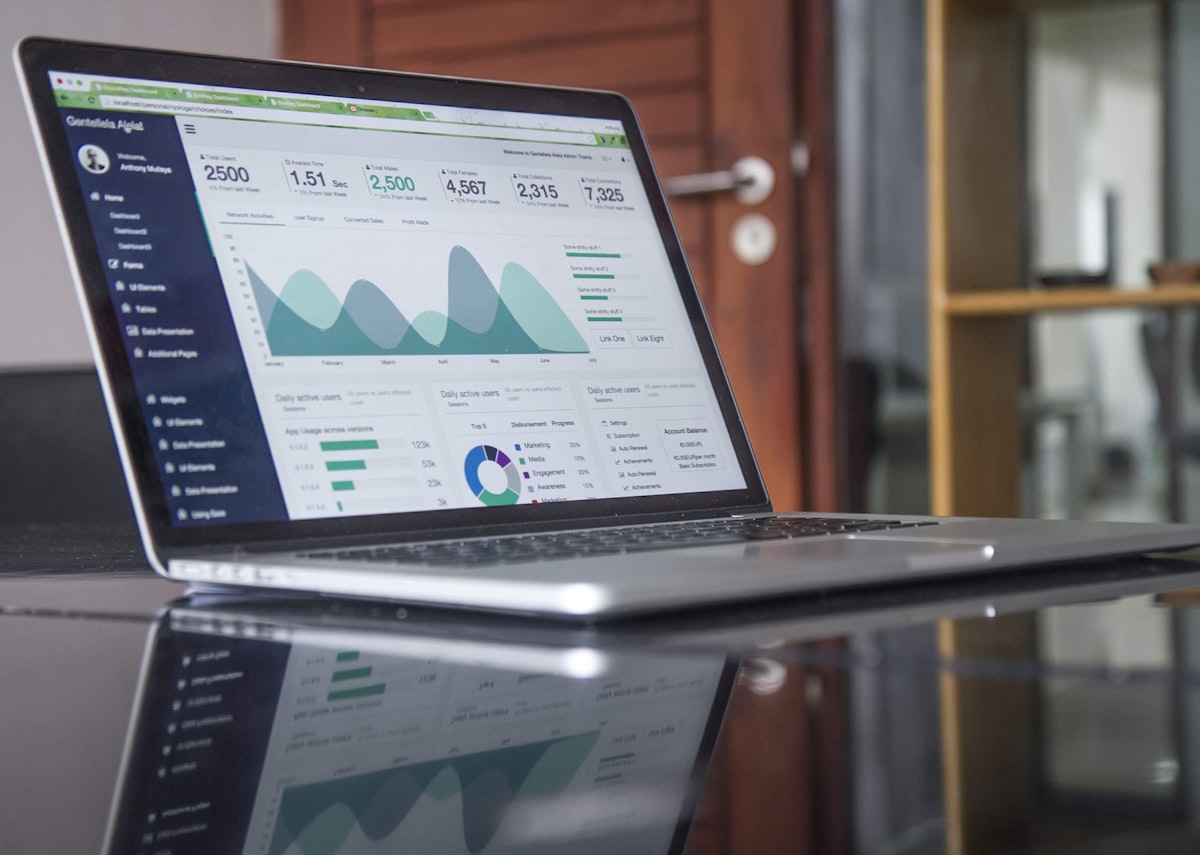
ติดตั้ง Elasticsearch และ Kibana บน VPS
Elasticsearch เป็น search engine และ analytics platform ที่ทรงพลัง ใช้สำหรับ full-text search บน application, log analytics (ELK Stack) หรือ real-time data pipeline Kibana เป็น UI สำหรับ visualize ข้อมูลใน Elasticsearch ต้องการ VPS ที่มี RAM อย่างน้อย 4GB จึงจะรันได้ดี
ติดตั้ง Elasticsearch 8
sudo apt update
sudo apt install apt-transport-https -y

# Import GPG key
wget -qO - https://artifacts.elastic.co/GPG-KEY-elasticsearch | \
  sudo gpg --dearmor -o /usr/share/keyrings/elasticsearch-keyring.gpg

# เพิ่ม repository
echo "deb [signed-by=/usr/share/keyrings/elasticsearch-keyring.gpg] \
  https://artifacts.elastic.co/packages/8.x/apt stable main" | \
  sudo tee /etc/apt/sources.list.d/elastic-8.x.list

sudo apt update
sudo apt install elasticsearch -y
# เริ่ม service
sudo systemctl enable --now elasticsearch
# บันทึก password ที่แสดงตอน install (ใช้ครั้งเดียว)
# หรือ reset password ใหม่
sudo /usr/share/elasticsearch/bin/elasticsearch-reset-password -u elasticตั้งค่า Elasticsearch สำหรับ Single-Node
sudo nano /etc/elasticsearch/elasticsearch.ymlcluster.name: my-cluster
node.name: node-1
network.host: 127.0.0.1 # bind localhost เท่านั้นสำหรับความปลอดภัย
http.port: 9200
# สำหรับ single node ปิด discovery
discovery.type: single-node
# ตั้ง JVM heap size (ครึ่งหนึ่งของ RAM แต่ไม่เกิน 30GB)
# แก้ใน /etc/elasticsearch/jvm.options.d/jvm.options
# -Xms2g
# -Xmx2gติดตั้ง Kibana
sudo apt install kibana -y
sudo systemctl enable --now kibana
sudo nano /etc/kibana/kibana.yml
server.host: "127.0.0.1"
server.port: 5601
elasticsearch.hosts: ["https://localhost:9200"]
elasticsearch.ssl.verificationMode: none # สำหรับ local dev# สร้าง enrollment token สำหรับ Kibana
sudo /usr/share/elasticsearch/bin/elasticsearch-create-enrollment-token -s kibanaทดสอบ Elasticsearch API
# Test connection
curl -k -u elastic:YOUR_PASSWORD https://localhost:9200

# สร้าง index
curl -k -u elastic:YOUR_PASSWORD -X PUT https://localhost:9200/products \
  -H "Content-Type: application/json" \
  -d '{"settings": {"number_of_replicas": 0}}'

# Index document
curl -k -u elastic:YOUR_PASSWORD -X POST https://localhost:9200/products/_doc \
  -H "Content-Type: application/json" \
  -d '{"name": "VPS Thailand", "price": 299, "category": "hosting"}'

# Search
curl -k -u elastic:YOUR_PASSWORD "https://localhost:9200/products/_search?q=vps"
Elasticsearch ต้องการ VPS ที่มีทรัพยากรสูงและ SSD ที่เร็ว สำหรับ server ที่รองรับ workload หนักแบบนี้ VPS สิงคโปร์จาก asiagb มี NVMe SSD และ RAM สูง เหมาะสำหรับ Elasticsearch และ analytics pipeline ก่อน production ควรตรวจ connectivity ของ cluster ด้วย dnsxray.com
ตรวจสอบว่า Elasticsearch ทำงานถูกต้อง
# ตรวจ cluster health
curl -k -u elastic:YOUR_PASSWORD https://localhost:9200/_cluster/health?pretty

# ดู nodes
curl -k -u elastic:YOUR_PASSWORD https://localhost:9200/_cat/nodes?v

# ดู indices ทั้งหมด
curl -k -u elastic:YOUR_PASSWORD https://localhost:9200/_cat/indices?v

# ดู logs
sudo journalctl -u elasticsearch -n 50green = ทุก shard ready, yellow = primary shard ready แต่ replica ไม่ assigned (ปกติสำหรับ single-node), red = บาง primary shard ไม่ ready มีปัญหา
แก้ปัญหาที่พบบ่อย
Elasticsearch ไม่ start ขึ้น — "max virtual memory areas vm.max_map_count too low"
Elasticsearch ต้องการ virtual memory มากกว่า default ต้องเพิ่ม kernel parameter:
sudo sysctl -w vm.max_map_count=262144
echo "vm.max_map_count=262144" | sudo tee -a /etc/sysctl.conf
sudo systemctl restart elasticsearch
Kibana ไม่ต่อ Elasticsearch ได้ — "Unable to retrieve version information"
Kibana 8 ต้องใช้ HTTPS กับ Elasticsearch การตั้ง HTTP ธรรมดาจะ fail ตรวจ config:
# ตรวจว่า Elasticsearch ใช้ HTTPS ไหม
curl -k https://localhost:9200  # ควรตอบสนอง (ใช้ -k สำหรับ self-signed cert)

# ถ้าใช้ HTTP (ปิด security ใน yml)
xpack.security.enabled: false  # dev only
Heap space error ทำให้ node crash
JVM heap ไม่พอ ปรับ Xms/Xmx ให้เหมาะกับ RAM ที่มี:
sudo nano /etc/elasticsearch/jvm.options.d/custom.options

-Xms1g   # minimum heap (1GB สำหรับ 4GB RAM VPS)
-Xmx1g   # maximum heap (ต้องเท่ากับ Xms)

sudo systemctl restart elasticsearch
Query ช้ามากบน index ขนาดใหญ่
ไม่มี index บน field ที่ query บ่อย หรือ field type ผิด (text vs keyword):
# ดู mapping ของ index
curl -k -u elastic:PASS https://localhost:9200/myindex/_mapping?pretty

# เพิ่ม keyword field สำหรับ exact match + sort
PUT /myindex/_mapping
{"properties": {"category": {"type": "keyword"}}}
คำถามที่พบบ่อย
Elasticsearch ต้องการ RAM เท่าไหร่?
สำหรับ development: 2GB RAM พอรันได้ Production ที่มี data น้อย: 4GB, data ปานกลาง: 8-16GB กฎคือให้ JVM heap ครึ่งหนึ่งของ RAM แต่ไม่เกิน 30GB อีกครึ่งหนึ่งเป็น OS cache สำหรับ Lucene file system cache
ELK Stack กับ OpenSearch ต่างกันอย่างไร?
OpenSearch เป็น open-source fork ของ Elasticsearch ที่ AWS สร้างขึ้นหลัง Elastic เปลี่ยน license ฟีเจอร์ใกล้เคียงกัน ถ้าใช้ AWS ให้ดู OpenSearch Service ถ้า self-host บน VPS ทั้งสองใช้ได้
จะ secure Kibana ไม่ให้เปิดสาธารณะได้อย่างไร?
Bind Kibana บน localhost แล้วเข้าผ่าน SSH tunnel หรือตั้ง Nginx reverse proxy พร้อม Basic Auth หน้า Kibana ไม่ควร expose port 5601 สาธารณะโดยตรง